Response
Reimagined
Most organizations discover their response plan fails during a real incident. ChaosTrack lets you rehearse cyber attacks, outages, physical and crisis events with AI-generated exercises, then responds automatically when real threats strike — turning chaos into execution.
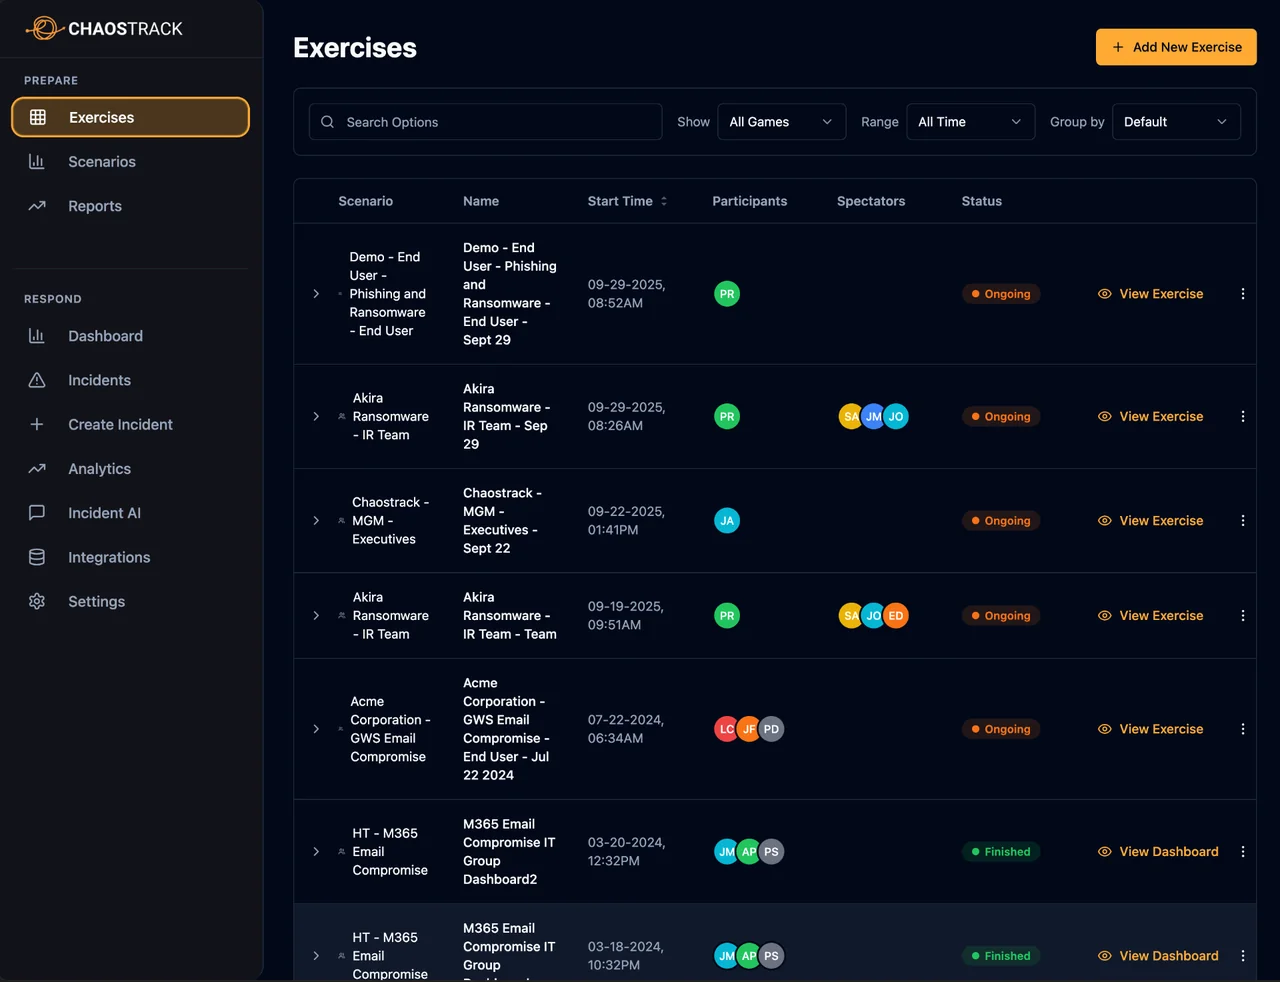
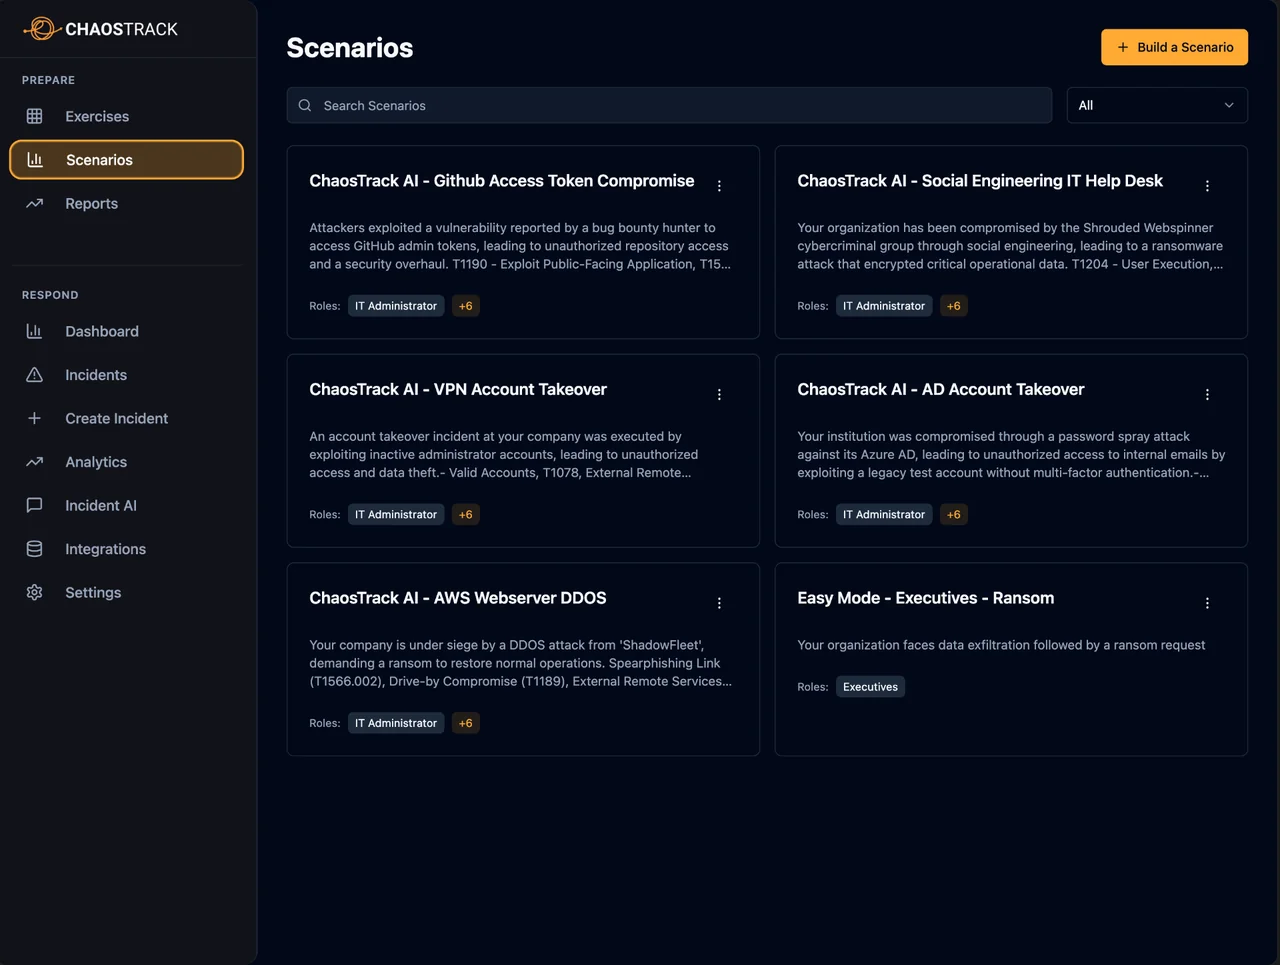
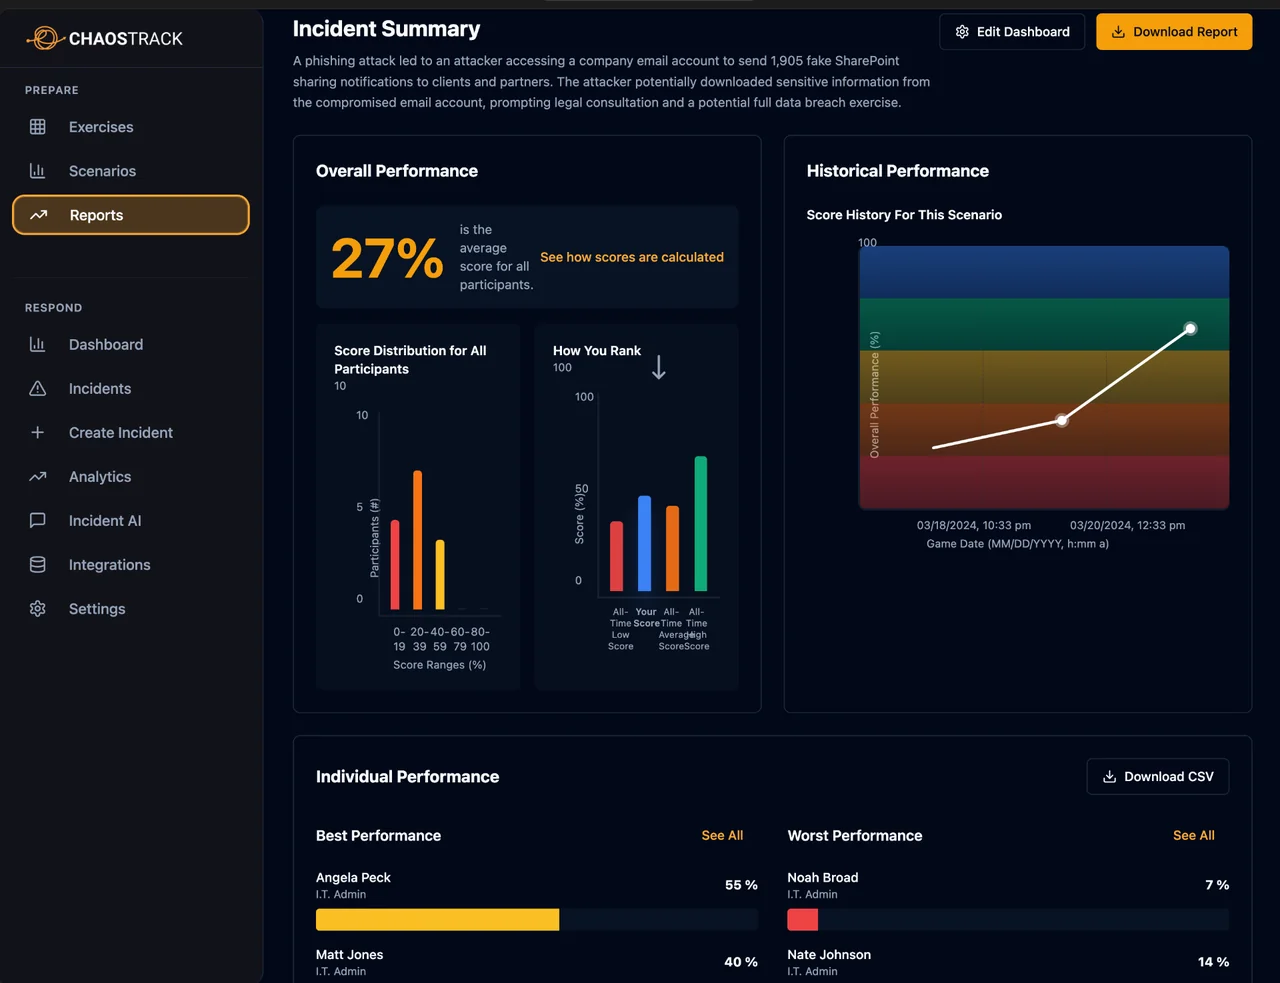
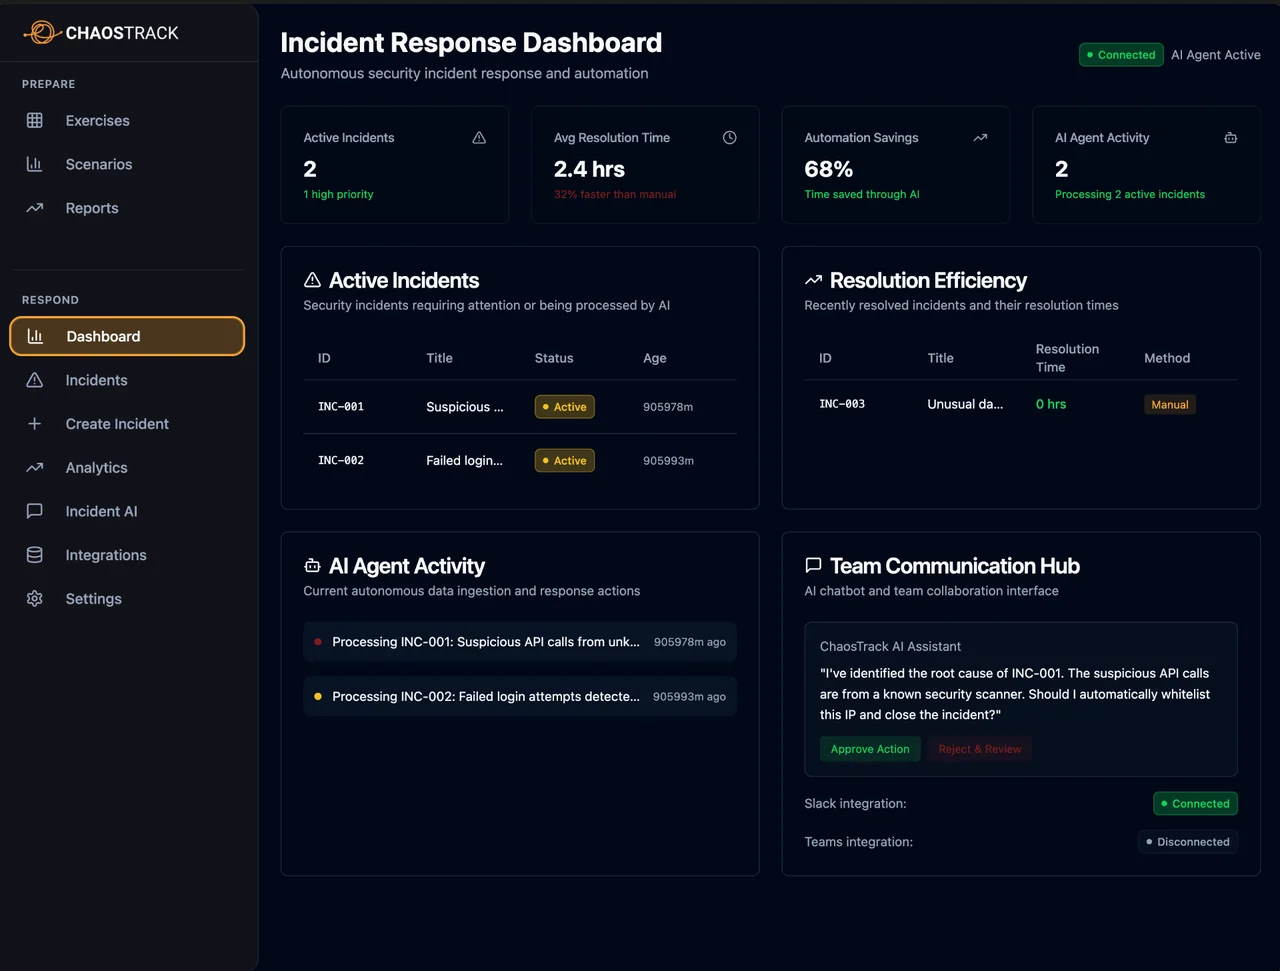
Prepare
AI-Powered Response Simulation
Don't assume. Simulate. Because 'pretty certain' doesn't mean prepared. Increase your cyber resilience with automated tabletop exercises that engage your whole company and test real-world incident response capabilities.
Simulate & Test Against Real World Attacks
Raise awareness, improve coordination, find gaps in your organization's security posture, validate assumptions, and ultimately build confidence.
Rapid Deployment
Set up realistic incident scenarios in minutes, not weeks. Reduce preparation time by 85% while improving training effectiveness.
Measurable Improvement
Track your team's progress with detailed analytics and insights that drive continuous security posture enhancement.
Respond
Autonomous Incident Response
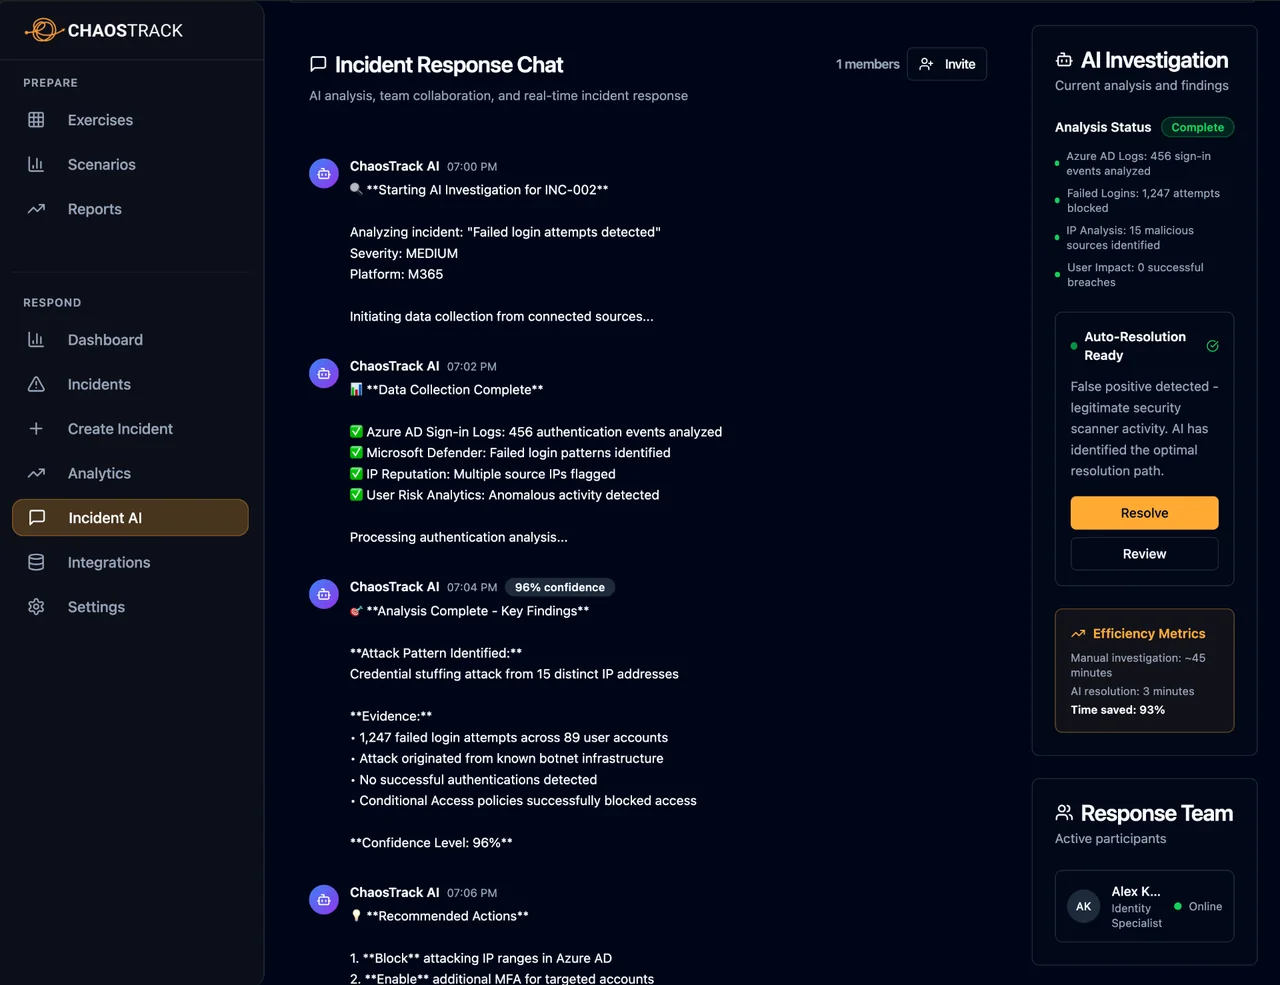
Next-generation AI-native incident response that transforms your incident response capabilities. From investigation to remediation, our autonomous platform operates continuously to respond to incidents without human intervention.
Autonomous Response
AI-driven incident response that operates 24/7, investigating, mitigating, and responding to incidents without human intervention.
Intelligent Response
Advanced machine learning algorithms that continuously learn from incidents to improve response coordination and effectiveness.
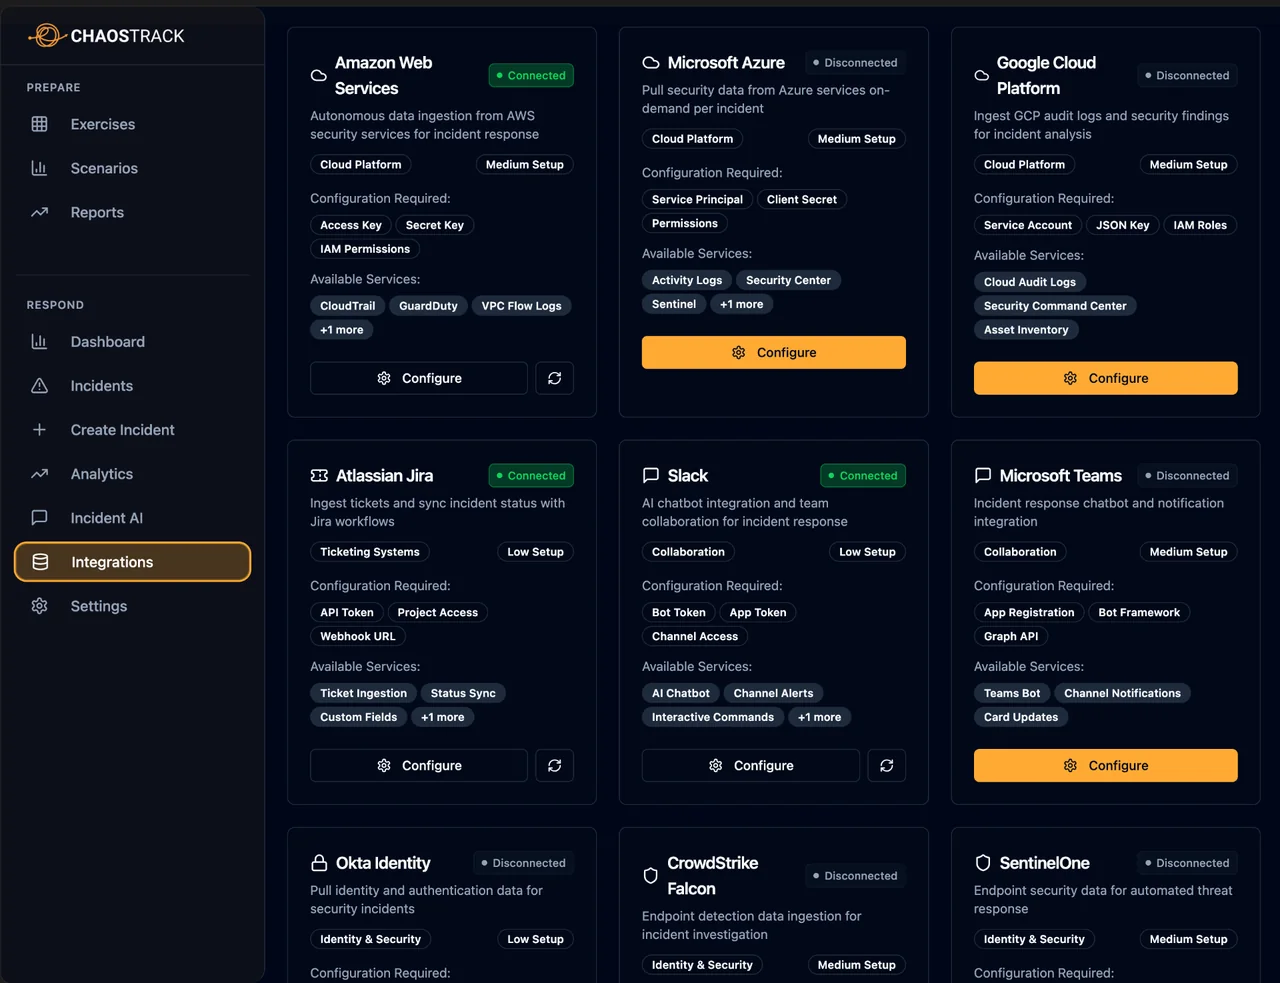
Precision Orchestration
Seamlessly coordinate response across your entire security stack with automated workflow orchestration.
 SlackTeamsConsole
Hunt
AI Threat Hunting
Proactive, always-on threat hunting that connects the dots across your environment. Investigate adversary behavior, correlate evidence and turn confirmed findings into action — available on its own or alongside Autonomous Incident Response.
Hypothesis-Driven AI Hunts
AI agents generate, test and refine threat hypotheses against your telemetry to surface adversary behavior.
Cross-Source Correlation
Connect signals across endpoint, identity, cloud, SaaS, network and email to investigate multi-stage attacks.
From Findings to Response
Build evidence chains and hand confirmed findings to your team or Autonomous Incident Response for containment.
What the Experts Say
Simulations are critical for real-world readiness and compliance.
IBM Cost of a Data Breach Report 2025
Companies that test their Incident Response plan contain breaches 48 days faster and save $1.49 million on the cost of a data breach.
Corporate Compliance Insights
Companies seeking to avoid a state Attorney General investigation should establish a schedule for simulations now, before a breach occurs.
SEC Incident Disclosure Rule December 2023
As time is of the essence, a well-practiced IR program will be critical.
It's about how well it can be executed.
Cybersecurity Industry Research
Organizations using automated incident response reduce mean time to containment by 74% and lower overall breach costs through consistent, rapid threat mitigation.
Understand How to Respond Under Pressure and at Speed
Test Your Plan
Simulate real-world scenarios and practice critical steps including detection, assessment, escalation, response, and coordination.
Test Your Team
Identify your superstars who can help with training, and areas where team members struggle with incident response tools and procedures.
Deploy AI Response
Implement autonomous incident response that operates 24/7, reducing response times and ensuring consistent threat mitigation.
Ready to Transform Your Incident Response?
See how ChaosTrack helps teams prepare for and respond to incidents. From AI-powered simulations to autonomous response - experience the complete platform that works at machine speed with human intelligence.
See ChaosTrack in action • No commitment required • Setup in minutes